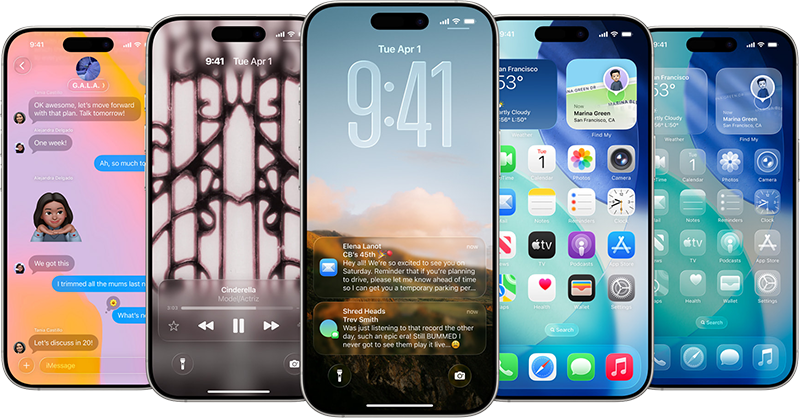
 Apple heeft een update voor versie 27 van iOS uitgebracht. In iOS 27, dat geschikt is voor de iPhone 11 en hoger, heeft Apple onder meer extra AI-functies beschikbaar gemaakt, zijn er meer mogelijkheden voor ouders om hun kinderen te beschermen en zijn er diverse verbeteringen in Liquid Glass aangebracht. In versie 27.2.1 zijn diverse beveiligingsproblemen verholpen.
AirPlayAvailable for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
App Intents
Impact: An attacker in Bluetooth range may be able to bypass the rate limit on pairing code attempts
Description: A logic issue was addressed with improved state management.
CVE-2026-113968: AppleAvailable for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Bluetooth
Impact: An app may be able to access sensitive user data
Description: An authorization issue was addressed with improved state management.
CVE-2026-113963: László VáradyAvailable for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
brotli
Impact: An attacker in Bluetooth range may be able to corrupt process memory
Description: A use-after-free issue was addressed with improved memory management.
CVE-2026-113970: AppleAvailable for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
CoreUtils
Impact: Processing maliciously crafted input may lead to memory corruption
Description: An out-of-bounds write issue was addressed with improved input validation.
CVE-2026-111497Available for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
CoreUtils
Impact: A malicious Bluetooth device may be able to establish a pairing without user interaction
Description: This issue was addressed with improved checks.
CVE-2026-113965: AppleAvailable for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Messages
Impact: An attacker in Bluetooth range may be able to bypass the rate limit on pairing code attempts and pair with a device without user interaction
Description: A logic issue was addressed with improved state management.
CVE-2026-113964: an anonymous researcherAvailable for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Messages
Impact: A remote attacker may be able to join an iMessage group chat and receive its messages
Description: An authorization issue was addressed with improved validation.
CVE-2026-113961: an anonymous researcherAvailable for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
rapportd
Impact: A user added to an iMessage group may be able to access messages sent before they joined
Description: This issue was addressed by removing the vulnerable code.
CVE-2026-113960: an anonymous researcherAvailable for: iPhone 11 and later, iPad Pro 12.9-inch 4th generation and later, iPad Pro 11-inch 2nd generation and later, iPad Air 4th generation and later, iPad 9th generation and later, and iPad mini 6th generation and later
Impact: An attacker on the same network may be able to bypass the rate limit on AirPlay pairing code attempts
Description: A logic issue was addressed with improved state management.
CVE-2026-113969: Apple








 apple support gesproken, denkt dat aan screenprotector ligt. (hoezo werkt scherm wel weer nadat je op de uit/aan knop dukt?)
